Is Public Wi-Fi Safe? What Really Happens When You Connect at the Airport
You land after a nine-hour flight. Your phone is on 18% battery, you have no local data, and your connecting gate has just been changed to something on the other side of the terminal. You open the Wi-Fi list, and there it is: Airport_Free_WiFi. No password. One tap and you're online.
Almost everyone taps. And almost every time, nothing bad happens — which is precisely why the habit sticks.
But "almost every time" is carrying a lot of weight in that sentence. Airports, hotels and train stations are among the few places left where a complete stranger can quietly position themselves between you and the internet, and where the cost of getting it wrong isn't a slow page load — it's a drained account or a hijacked email address that takes months to clean up.
This guide is meant to be an honest one. A good deal of what gets written about public Wi-Fi is a decade out of date, and some of it was never anything more than scare marketing from companies selling VPN subscriptions. So let's go through what has genuinely changed, which risks are still real in 2026, and what's actually worth doing about them.
Why public Wi-Fi is a different animal from your home network
At home, three things are quietly working in your favour. You know who owns the router. The connection between your devices and that router is encrypted with a password only your household has. And nobody else is on the network.
Open public Wi-Fi throws away all three.
You cannot verify the network is what it claims to be. This is the big one, and it surprises people. A Wi-Fi network name is just a label that any device can broadcast. There is no registry, no verification, no certificate. If your phone shows you a network called Heathrow_Free_WiFi, that tells you exactly as much as a stranger in a high-vis vest telling you they work here.
On a truly open network, the radio traffic isn't encrypted. Anyone within range with the right software can see the shape of what everyone nearby is doing — which sites, which apps, how much data, at what times. Not necessarily the contents, but more than you'd guess.
Whoever runs the network sees your traffic pass through. Even a perfectly legitimate airport hotspot operator is sitting in the middle of your connection. Whether that matters depends entirely on who they are and what their terms of service permit them to do with what they see.
What actually changed: half the old advice is now wrong
Around 2010, a developer released a Firefox extension called Firesheep. It let anyone sitting in a café click a name in a sidebar and take over that person's Facebook or Twitter session. It wasn't sophisticated. It worked because most websites at the time only encrypted the login page and sent everything afterwards in plain text.
That world is gone. The overwhelming majority of web traffic is now encrypted end to end with HTTPS. Your browser warns you loudly when a site isn't. Apps pin their certificates. DNS lookups are increasingly encrypted too. The classic image of a hoodie-wearing figure at the next table quietly reading your banking password out of the air is, in 2026, largely a historical artefact.
Here's the part that matters, though: the risk didn't disappear. It moved. Attackers stopped trying to eavesdrop on encrypted traffic — because that's genuinely hard now — and started doing something far easier. They get you to hand things over voluntarily.
The risks that are still real
The evil twin: a fake network wearing the airport's name
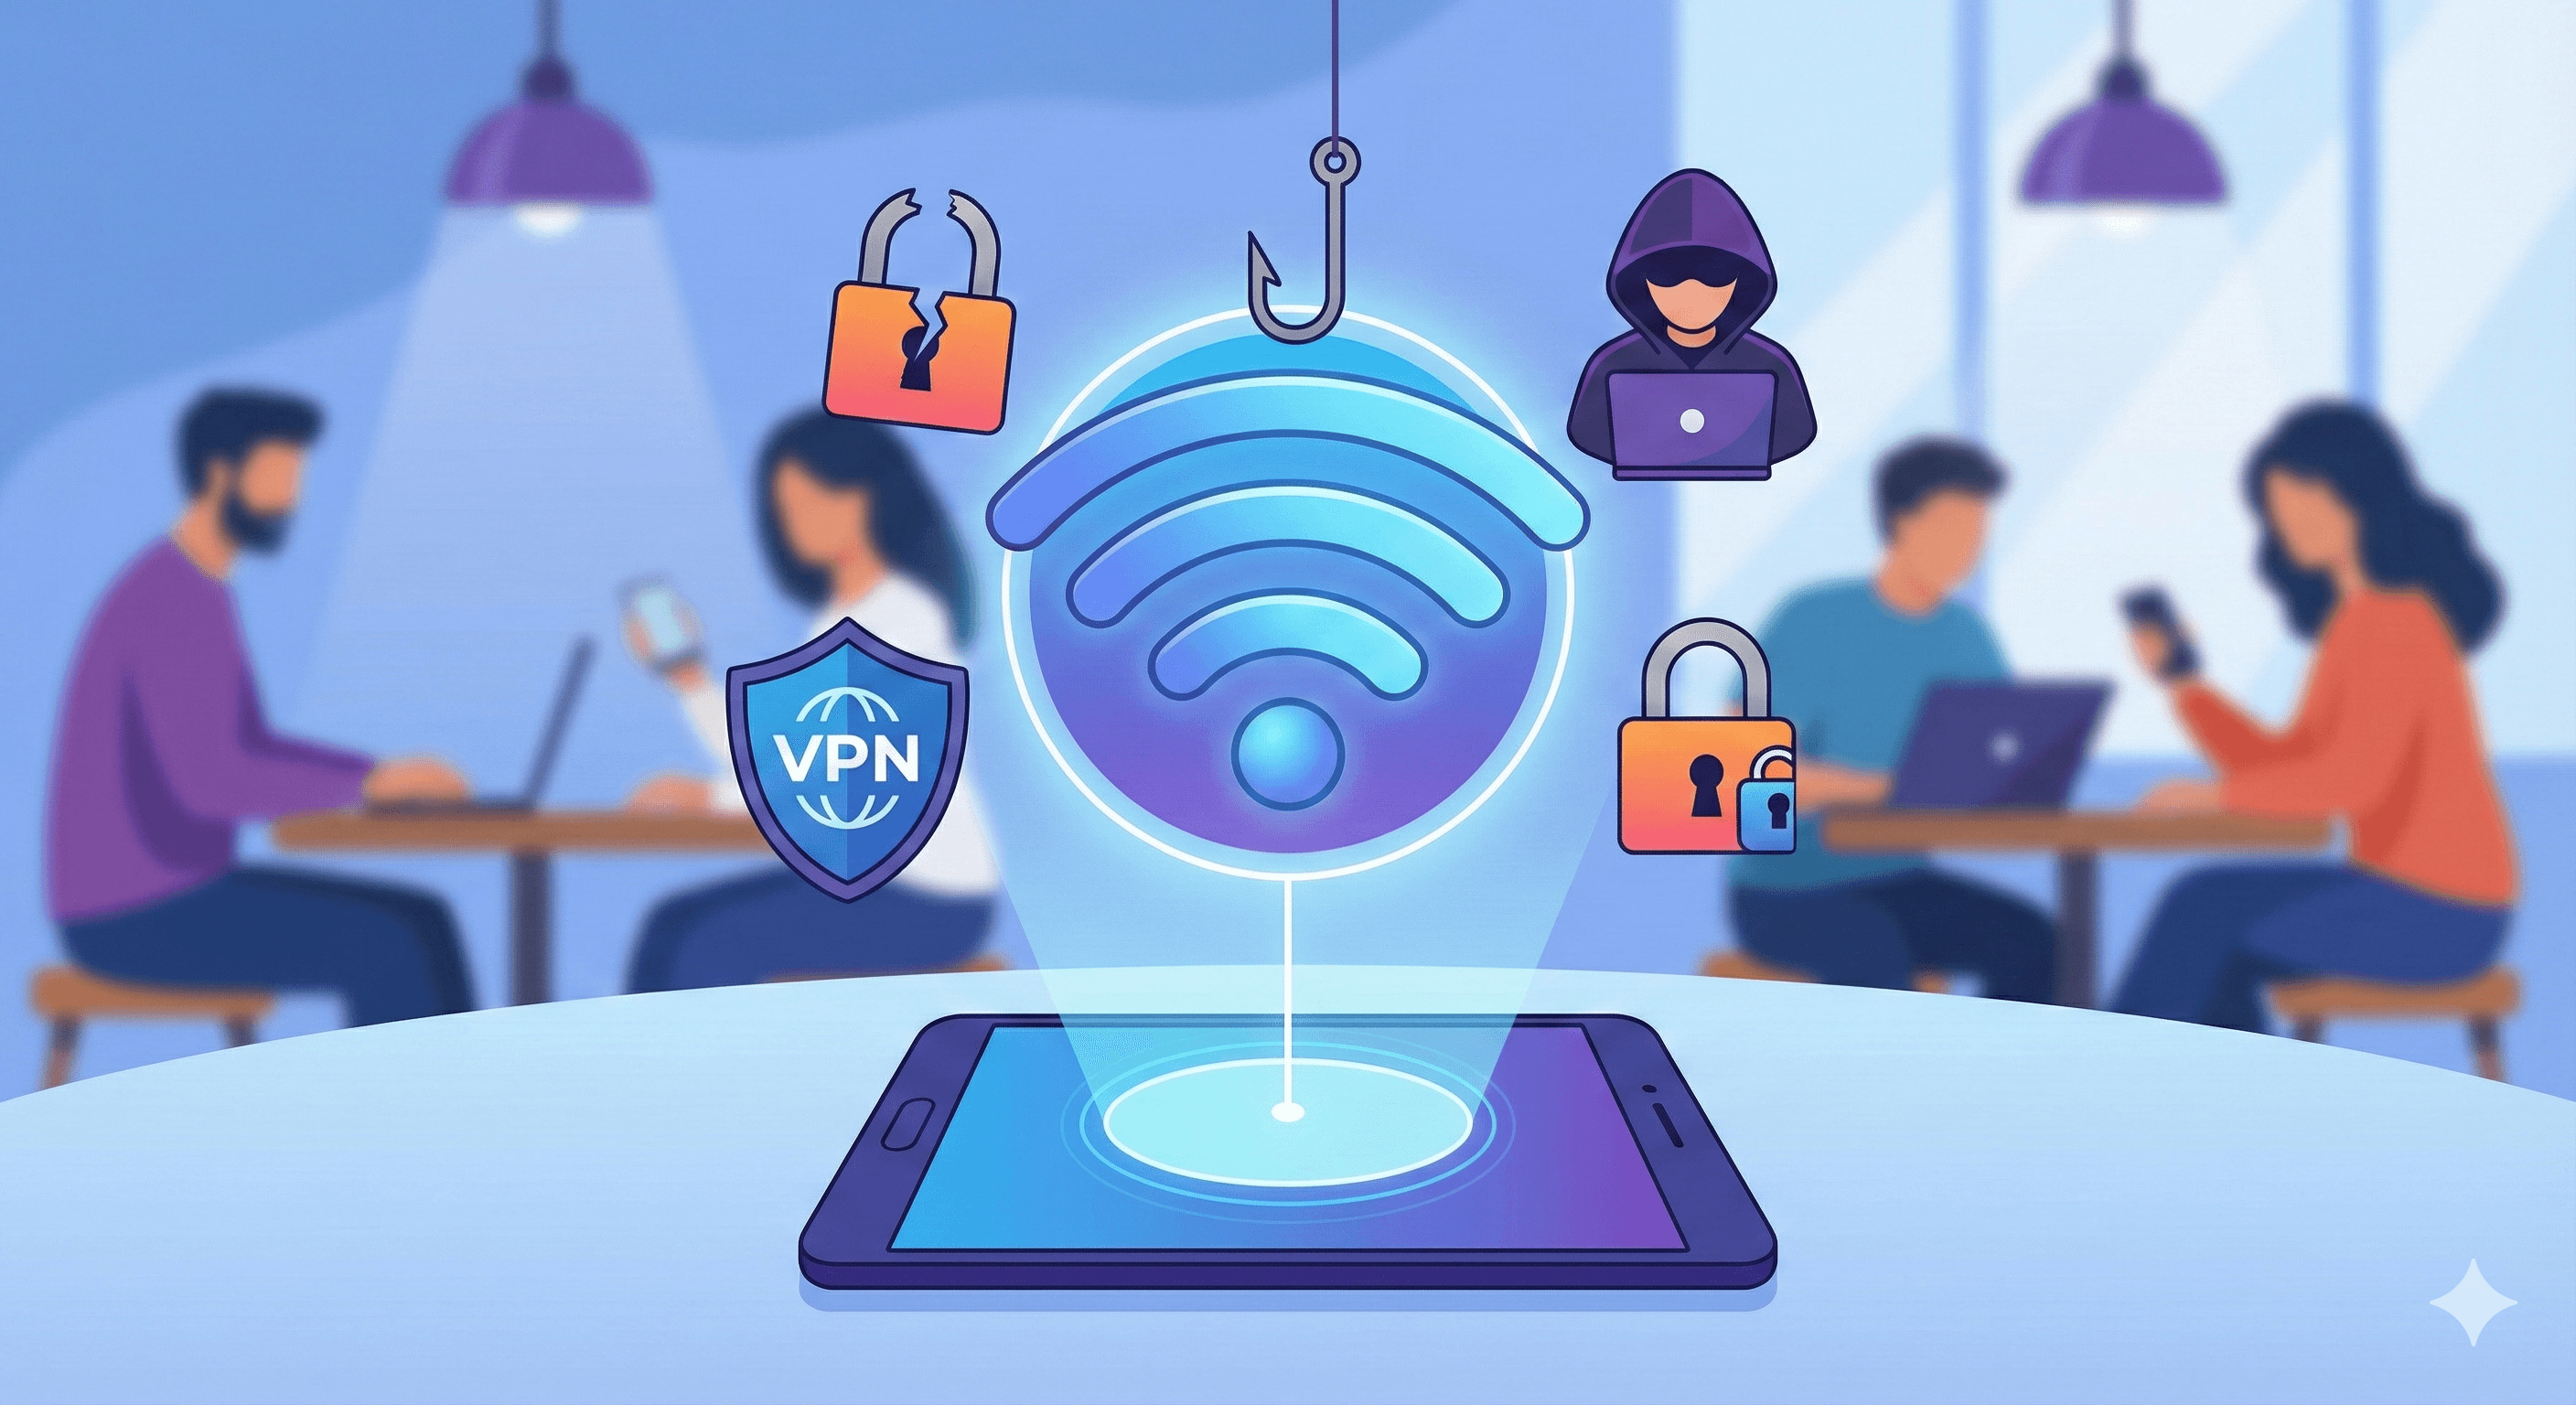
The hardware to broadcast a Wi-Fi network costs less than a decent dinner and fits in a jacket pocket. Set it up in a departure lounge, name it something plausible — Free_Airport_WiFi, Terminal2_Guest, the actual name of the airport's real network with an underscore moved — and wait. Phones searching for the strongest open signal will find it. Some will join automatically.
Once you're on that network, its operator controls what your phone considers "the internet". They decide which page loads when you type an address. They decide what your device is told when it checks for updates. They can't break HTTPS, but they don't need to — they only need you to make one trusting decision.
Fake captive portals: the most effective airport attack there is
A captive portal is that login page that appears when you join a public network. Real ones typically ask for an email address, a room number, or just a click on "I accept".
Fake ones ask for a little more. Card details, "for age verification — you won't be charged". Your passport or booking reference. Or, most damaging of all, a "Sign in with Google" button that leads to a convincing replica of Google's login page.
This works so well because it inverts your instincts. Normally an unexpected request for your card details would set off alarms. But here, you're expecting a login screen. You asked for it. It appeared exactly when it should have. Your guard is already down, and you're tired, and your gate closes in twenty minutes.
No legitimate airport, hotel or café network will ever need your card number, your passport number, or your email password to give you internet access. Not one. If a portal asks, the network is either hostile or so aggressively commercial that you should walk away regardless.
"Download our app to connect"
Occasionally a real hotel chain does this, which is unfortunate, because it trains people to accept the pattern. At an airport, treat it as an immediate no. Installing software handed to you by a network you can't verify undoes every other precaution in this article.
Certificate warnings you're tempted to click through
If a hostile network tries to intercept an encrypted connection, your browser will notice and throw up a full-page warning — usually red, usually alarming, usually with a small "proceed anyway" link buried at the bottom.
That warning is the system working exactly as designed. On a public network it should be treated as a hard stop, every single time. There is no legitimate reason for a certificate error on your bank's website in an airport lounge.
Networks that harvest you entirely legally
Not every risk is criminal. A significant share of "free" public Wi-Fi is run by advertising businesses. The deal is stated plainly in terms of service nobody reads: you get bandwidth, they get your email address, your device identifier, your rough location over time, and permission to build a profile and sell access to it.
Nothing is stolen. You agreed. It's just that the price wasn't zero, and it wasn't obvious.
Hotel Wi-Fi, which is quietly worse than airport Wi-Fi
Hotels get less attention than airports and often deserve more. The credentials are frequently your room number and surname — information printed on the envelope your key card came in. The equipment is sometimes a decade old and rarely patched. And on many hotel networks, guest devices can see each other, meaning an infected laptop three floors up is on the same segment as your phone.
You're also more relaxed in a hotel. You unpack, you sit down, you finally deal with that bank transfer you've been putting off. It's the environment where people do their most sensitive browsing on their least trustworthy connection.
How to use public Wi-Fi without getting burned
If you're going to connect anyway — and sometimes you are — these are the habits that actually matter, roughly in order of how much they buy you.
- Keep two-factor authentication switched on everywhere. This is far and away the highest-value thing on this list. Almost every realistic attack ends with someone holding a password they can't use, because they don't have your second factor. If you do nothing else, do this.
- Ask a member of staff for the exact network name. Ten seconds at a service desk defeats the evil twin entirely. Note that it's the exact name that matters — attackers rely on you not noticing an extra underscore.
- Turn off automatic joining of open networks. On iPhone, Settings → Wi-Fi → Ask to Join Networks, and switch off Auto-Join for individual networks. On Android it's under Wi-Fi preferences. This stops your phone silently connecting to something in a corridor while it's in your pocket.
- Treat every login page as hostile until proven otherwise. Email address or room number: fine. Card details, passport number, or a social login button: close it and leave.
- Never click through a certificate warning. Not once, not "just this time".
- Postpone anything genuinely sensitive. Banking, tax portals, anything involving a payment. It will keep for an hour.
- Forget the network when you're done. Otherwise your phone will hunt for it in every city you visit afterwards — and anyone can broadcast a network with that name.
- Turn off file sharing and set AirDrop to contacts only. Ten seconds, removes an entire nuisance category.
- Keep your operating system updated. Boring, unglamorous, and the reason most known attacks don't work on you.
Does a VPN actually help?
Yes, for one specific thing, and it's worth being precise about what that thing is.
A VPN wraps everything leaving your device in an encrypted tunnel to a server elsewhere. To the airport network — or to an evil twin — your traffic becomes meaningless noise. That genuinely neutralises passive snooping and interception.
What it doesn't do is more important to understand:
- It cannot help if you type your card number into a fake portal. You handed the data over; encryption of the delivery route is irrelevant.
- It doesn't stop you installing malicious software.
- It doesn't make you anonymous, whatever the sponsorship reads say.
- It moves your trust rather than removing it — from the airport operator to the VPN provider. With a free VPN, that's usually a downgrade. Free VPN apps have a long, well-documented history of logging and selling exactly the traffic they promised to protect.
A reputable paid VPN is a reasonable tool. It is not a shield that makes public Wi-Fi safe, and treating it as one tends to make people less careful, not more.
The simplest fix: skip public Wi-Fi entirely
Every risk described above shares a single root cause: you connected to a network you couldn't verify, operated by someone you can't identify.
Use your own mobile data and that root cause disappears. Not mitigated — gone.
Mobile networks work in the opposite direction from public Wi-Fi. Your SIM authenticates with the network cryptographically, so a stranger can't impersonate a mobile operator the way they can impersonate a hotspot. The connection between your phone and the tower is encrypted by default. There's no login page, so there's nothing to fake. And you're not sharing a network segment with a few hundred strangers.
The old obstacle was cost. Roaming charges abroad used to be punishing enough that free Wi-Fi looked like the only sane option. That's the part that's changed. A travel eSIM is a digital SIM you install on your phone before you leave, usually within a couple of minutes, without swapping out the card that carries your normal number. You land, the data is already working, and you walk past the free Wi-Fi without opening the list.
If you're not sure whether your phone supports one, our compatible devices list covers every current model, and if you're new to the technology, this explainer is a good starting point.
To be fair about it: mobile data isn't magic. Your operator still sees metadata, and no connection is beyond scrutiny. But it removes the entire class of attacks that depends on you trusting a stranger's network — and at an airport, that's essentially all of them.
Quick answers
Is it safe to check my bank balance on airport Wi-Fi?
The app itself is well protected and the connection is encrypted, so it's not the catastrophe it once was. But if you can wait until you're on mobile data, wait. There's no upside to doing it on a network you can't verify.
Is a password-protected network safer than an open one?
Somewhat — the radio traffic is encrypted, so casual eavesdropping is off the table. But if the password is printed on a sign behind the counter, everyone in the building has it, including whoever you're worried about. It raises the floor, not the ceiling.
Can someone hack my phone just because we're on the same Wi-Fi?
Not simply by being on the same network, no. A modern, updated phone doesn't accept unsolicited connections from other devices. The risk comes from what you're persuaded to do — a fake page, a dismissed warning, an installed app — rather than from proximity alone.
Should I use my phone's hotspot instead of the hotel Wi-Fi?
Yes, and it's an underrated move. Tethering your laptop to your phone puts everything on your own mobile connection. If you're travelling with a data plan that has room in it, this is the easy answer for working from a hotel room.
What about public charging ports?
Documented attacks through USB charging points exist but remain rare, and modern phones ask before granting data access over USB. Say no to that prompt and charge away. A cheap power bank sidesteps the question entirely.
The short version
- The old fear — someone reading your password out of the air — is mostly obsolete. HTTPS fixed it.
- The current risk is deception: fake networks, fake login pages, and things you're persuaded to type in yourself.
- No legitimate free network needs your card number, passport number or email password.
- Two-factor authentication protects you more than anything else on the list.
- A VPN encrypts the route. It doesn't protect you from your own trusting tap.
- Your own mobile data removes the problem at its root, and a travel eSIM makes that affordable in a way it wasn't a few years ago.
The next time you land somewhere unfamiliar and that free network appears at the top of the list, the question worth asking isn't whether it's dangerous. It's whether you actually need it.